Don't Just Replace Kenna- Evolve to Vulnerability Exposure Management



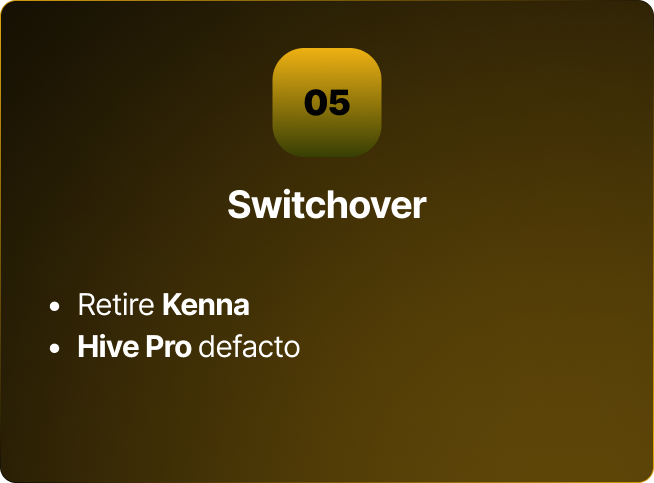
Cisco has announced the end-of-sale for Cisco Vulnerability Management (formerly Kenna Security), leaving security teams with a critical decision: remain on a legacy path or transform.
Yes, it is true that the Kenna Security platform will be supported until June 30th, 2028 but the platform won’t be keeping in pace with the evolving requirements of the customers while the threat landscape and tactics will continuously be evolving. This imbalance will put the security teams and leaders at a disadvantage.
This is the reason, don’t treat this as just a moment to make a lateral change with the solution you’ll use, it's an opportunity to transform how you approach and manage risk.
Why A Lateral Replacement Won’t Help
When your reliable sedan reaches end-of-life, you don't just buy another sedan from 2015. You look at what's available now, an electric vehicle with better range, smarter safety features, and lower operating costs.
Simply replacing Kenna with another (Risk-based vulnerability management) tool, or RBVM, is like trading your old car for another “old car”. You solve the immediate problem but miss the chance to leap forward and upgrade your Vulnerability Management Program.
Why Kenna Security No Longer Meets Your Needs Today:
1. Limited coverage :
Focused only on network infrastructure and applications—never expanded to cloud, containers, mobile apps, or open-source components
2. Theoretical risk scoring :
Relied on theoretical risk scores rather than validated exposures through real attack simulations
3. One-size-fits-all threat intelligence :
Applied global threat data without filtering for specific industries or geographies
4. No business context :
Failed to incorporate asset criticality based on what actually matters to your organization
5. Not recognized as a leading solution :
Cisco Vulnerability Manager (Formerly Kenna) is not included in the 2025 Gartner Magic Quadrant for Exposure Assessment Platforms (EAP)
What should you do to mitigate the risk from Kenna’s end of life announcement and legacy platform?
"Don’t wait. Act now to secure your future."
Businesses shouldn’t wait for the Kenna Platform to end support in June 2028 but should rather take a proactive approach in:
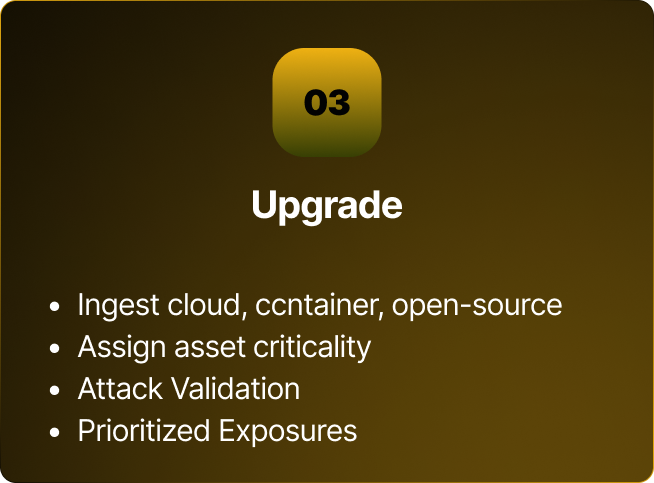
- Upgrading it to a more unified and comprehensive Vulnerability Exposure Management (VEM) platform with Hive Pro.
- Consolidating vulnerability scanning, prioritization, validation and mitigation in one platform- you no longer need a separate vulnerability scanning vendor.
Why Hive Pro Is the Right Upgrade Path
1. No Blind Spots
Eliminate vulnerability blind spots with highest CVE coverage in the industry
2. Targeted Threat Intelligence
Industry and geography-specific threat prioritization. Focus on attacks that actually target your sector and region.
3. Business-Context Aware
Prioritize based on asset criticality and business impact. Protect what matters most to your organization first.
4. Threat Actor Correlation
Connect CVEs to specific threat actors and active campaigns. Understand who's targeting you and how.
5. Validated Exposures
Real-world attack simulations evaluate security control effectiveness. Know what is truly exploitable, not just theoretically risky.
6. 360° Exposure View
Complete visibility across networks, applications, open-source software, cloud environments, and containers.
7. Flexible deployment
Choose between on-prem or cloud-based on your requirements
8. Vendor consolidation
Works with existing scanners or replaces them entirely for cost savings
9. Gartner™ recognized
Featured in the 2025 Magic Quadrant for Exposure Assessment Platform
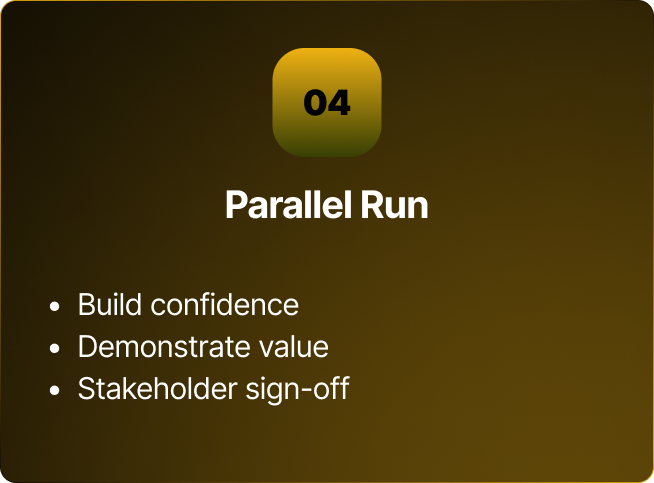
Transformation Journey

Please get in touch with us to discover how Hive Pro can make the Kenna to Hive Pro journey pain-free both technically as well as commercially, we are the right partner of choice.
[hubspot portal="44765325" id="f94a6c25-0c55-44d4-b79e-e47edddd545a" version="" type="form"]





